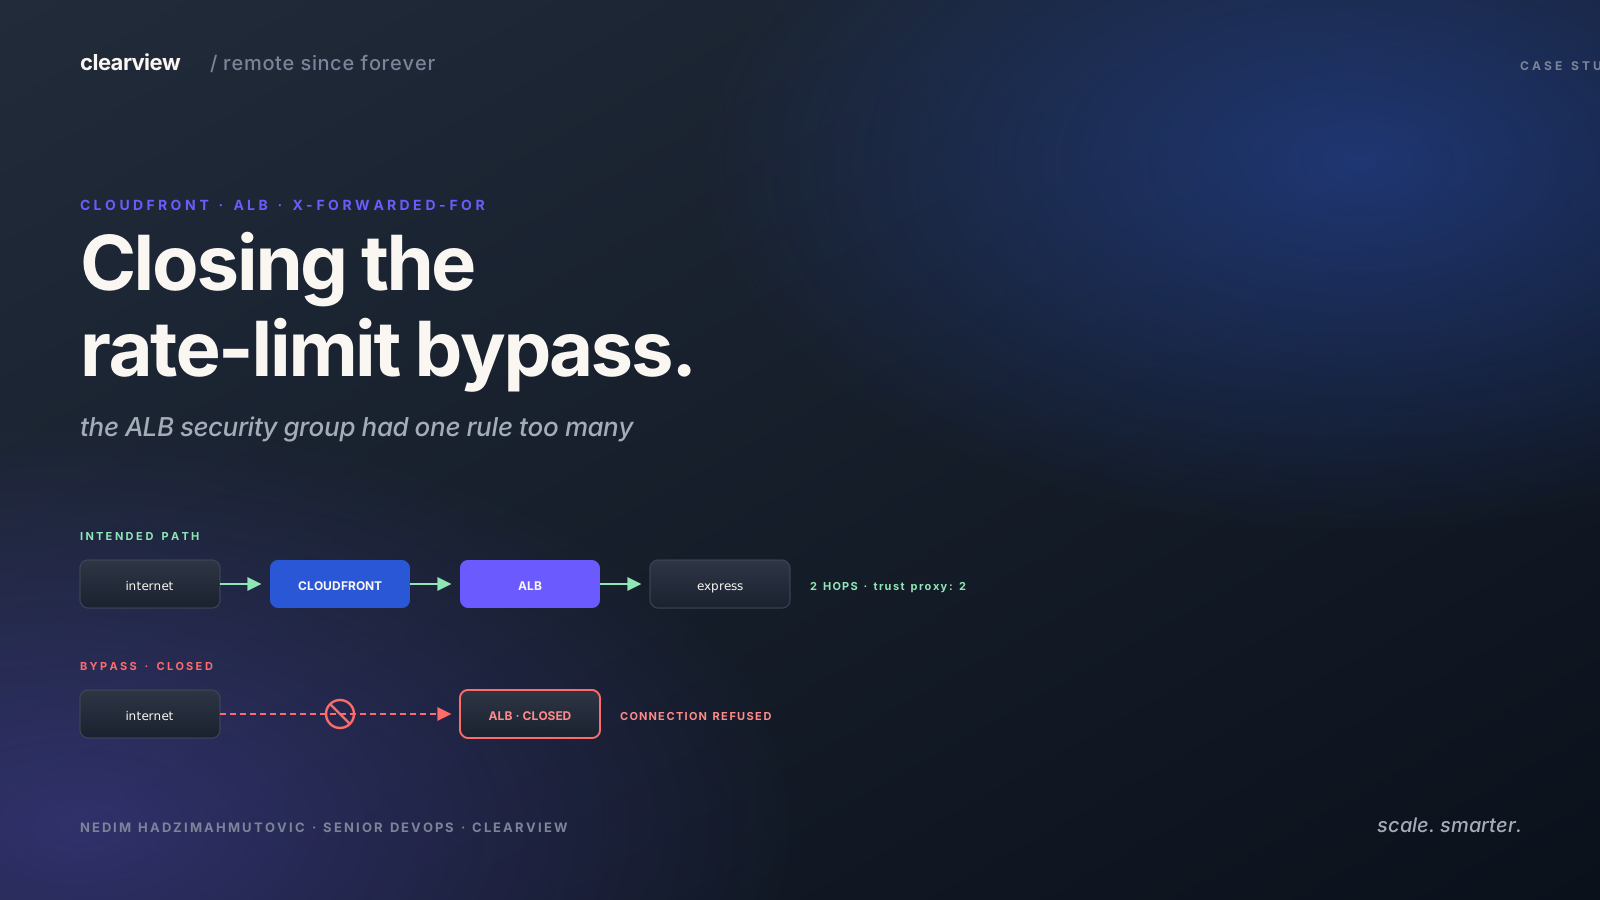
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
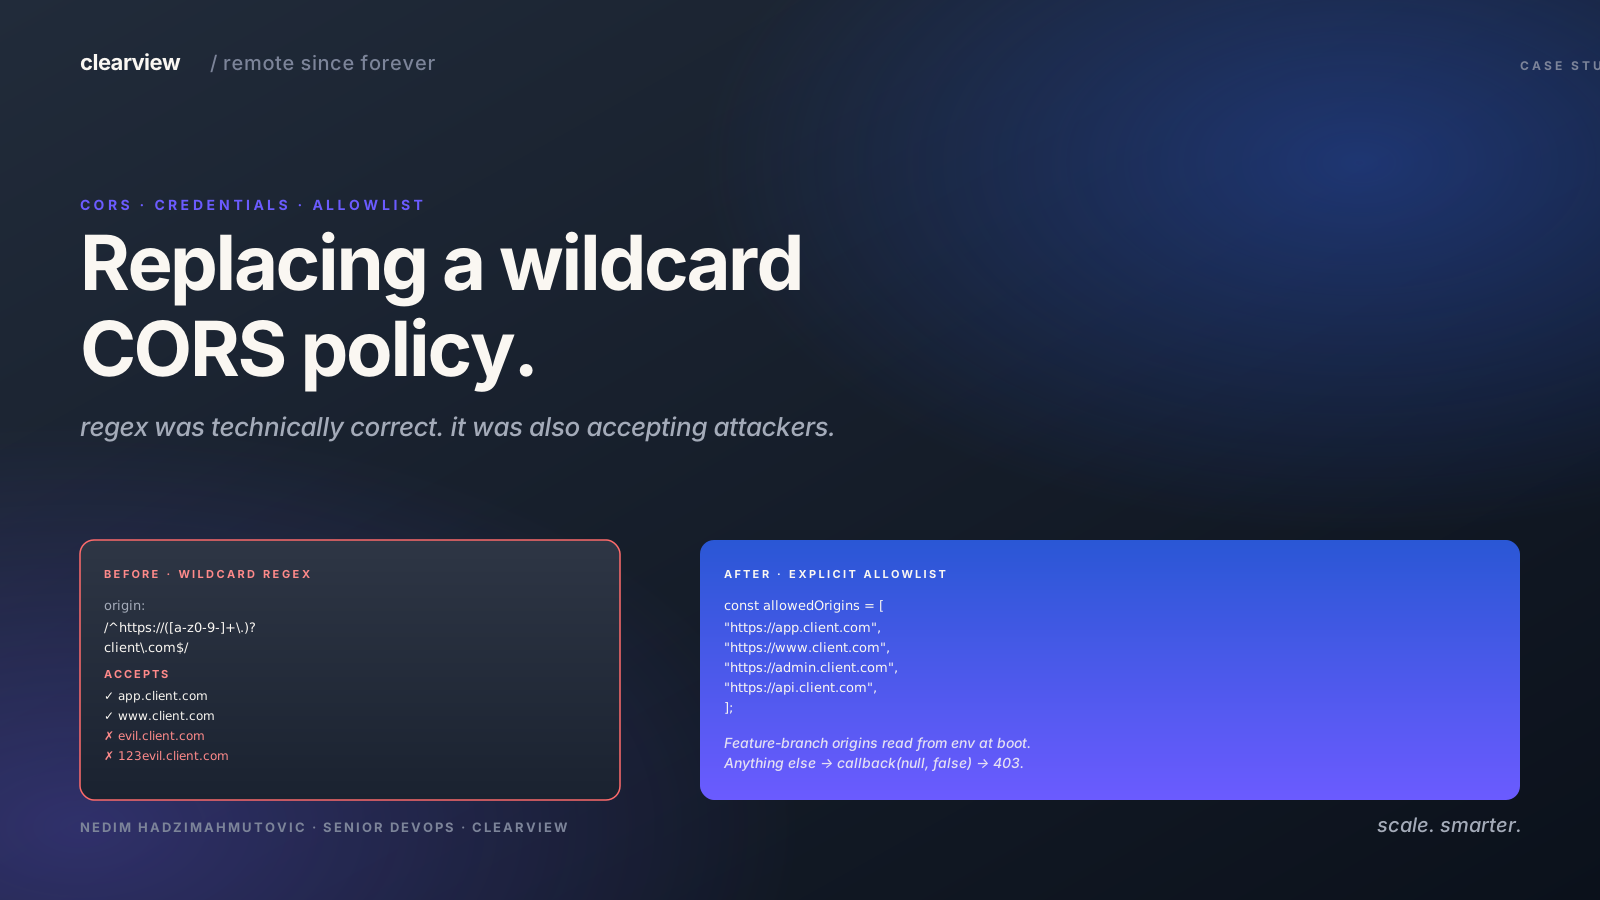
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
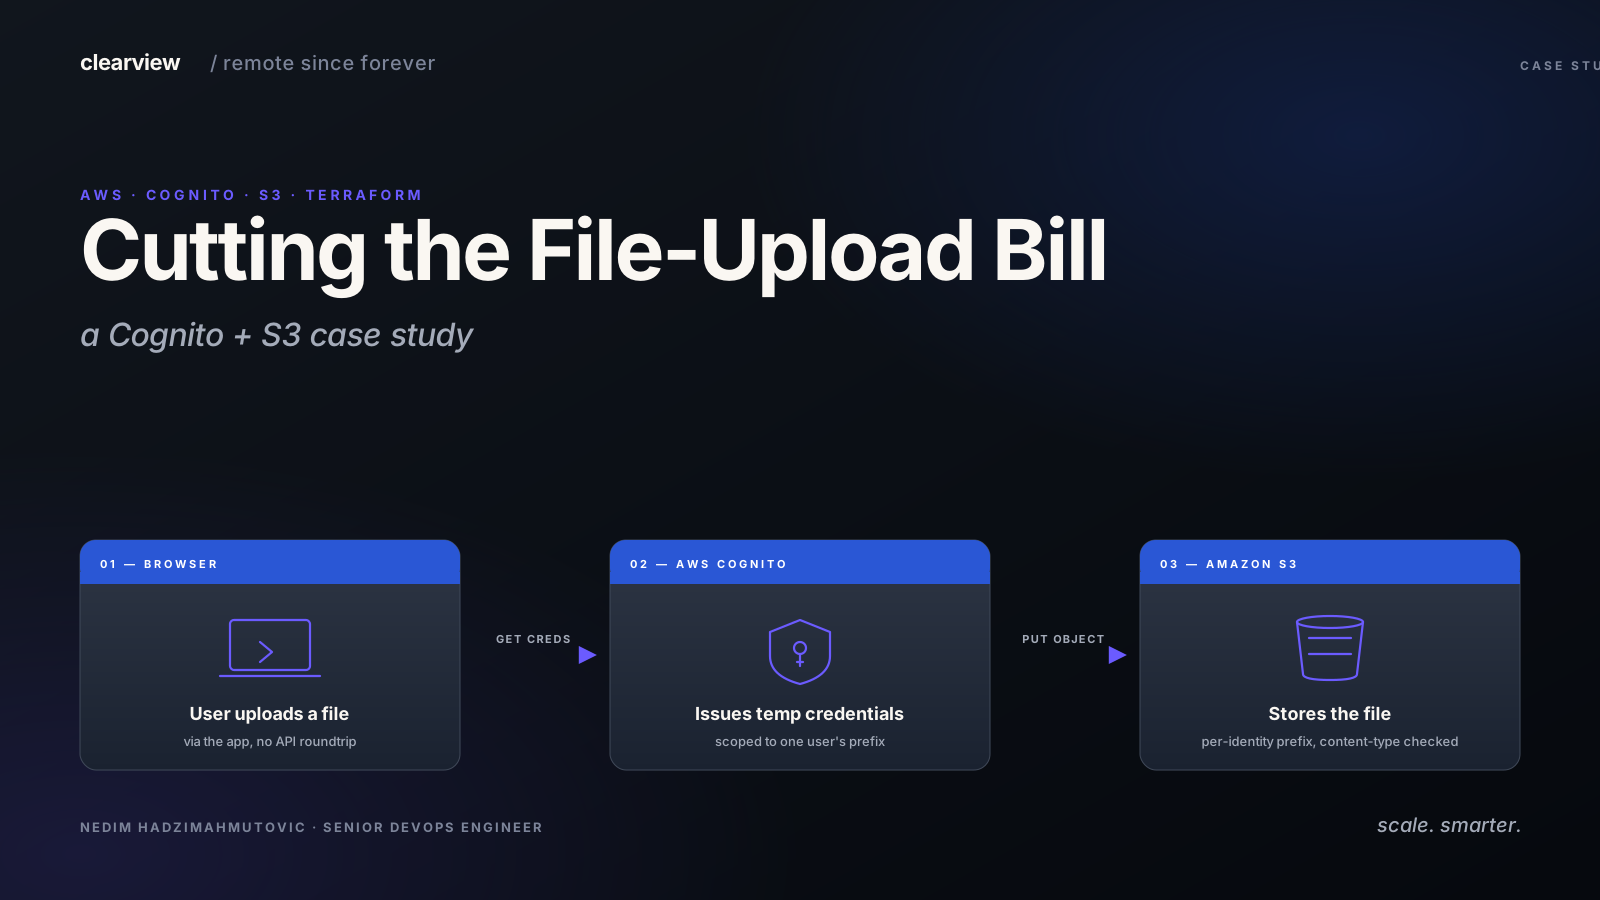
Cutting the File-Upload Bill: A Cognito + S3 Case Study
How we replaced a hosted upload widget with native Cognito and S3, kept the browser uploading straight to the bucket, and brought the monthly invoice down.

Upgrading TypeORM 0.3 to 1.0 in Production: A NestJS Case Study
How we took TypeORM 0.3 → 1.0 to a live NestJS API without a headache.

How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.

Implementing a Zero Auth Unsubscribe Link on Your Email
Nobody logs in to unsubscribe. They mark you as spam instead. Here's the small trick we used — a signed token in the URL — so users can unsubscribe with one tap without ever seeing a login screen.
Trending on Remote Since Forever


Case-Study Hubs
Real client engagements grouped by the shape of the work — pick a lane.
-
Case-Study Hub
Web API Security Case Studies
Case studies of Node.js Express API security findings — CORS allowlist, JWT audience map, X-Forwarded-For rate-limit, S3 IAM, CloudFront header leak.
-
Case-Study Hub
AWS Cost Optimization Case Studies
AWS cost optimization case studies — Graviton (ARM) up to 20% off compute, Compute Savings Plans up to 66% off, budget alerts before the invoice hits.
-
Case-Study Hub
Node.js Backend Refactor Case Studies
Case studies of refactoring a Node.js backend without downtime — mega-service split, TypeORM 1.0 upgrade, and migrations that keep production quiet.
-
Case-Study Hub
AWS DevOps Case Studies: Terraform, App Runner, WAF
AWS DevOps case studies — App Runner deploys, Terraform budgets and WAF, Cognito + S3 direct uploads, and an event-driven AWS architecture.
-
Case-Study Hub
Auth Architecture Case Studies
Case studies of auth architecture decisions: JWT audience maps, signed unsubscribe tokens, CloudFront JWT leaks, and silent cross-portal SSO with session barriers.
-
Topic Hub
Frontend & Mobile Engineering
Frontend and mobile engineering write-ups: React Native permission priming, shared fetch caching, drag-and-drop reordering, and CSS architecture decisions.
Case studies
View all 10-
aws
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
-
express
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
-
aws
Cutting the File-Upload Bill: A Cognito + S3 Case Study
How we replaced a hosted upload widget with native Cognito and S3, kept the browser uploading straight to the bucket, and brought the monthly invoice down.
Security & DevSecOps
View all 5-
aws
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
-
express
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
-
aws
How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.
AWS & Cloud
View all 6-
aws
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
-
aws
Cutting the File-Upload Bill: A Cognito + S3 Case Study
How we replaced a hosted upload widget with native Cognito and S3, kept the browser uploading straight to the bucket, and brought the monthly invoice down.
-
aws
How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.
Remote & team
View all 4-
remote
Escape From Slack Island
Working remotely doesn't have to feel like a life sentence in solitary. Here's how.
-
remote working
The Eight Virtues of Remote Bushidō: A Handbook For Digitally Nomadic Developers
A handbook for digitally nomadic developers — eight virtues that turn remote work from a perk into a discipline.


Software craft
View all 6-
gpt
Securing LLM — Retrieval Augmented Generation
Five steps to keep a RAG-powered LLM app from leaking its prompt, your data, or both.
-
software development
Power of AI in Software Development
How CVAI cut hours of JIRA grooming, PR creation, and PR review down to seconds for our engineering team.
-
business development
Clearview is now a verified member of the Pangea community
What our Pangea verification turned up about how Clearview engineers actually show up for clients.


See what else we've published
32 more-
backend
Splitting a Mega-Service Into Four: The Service-Facade Refactor (Plus a Reusable Skill)
How we split a 1,307-line `user.service.ts` into four responsibility-tagged NestJS sub-services (query, mutation, membership, stats) behind a stable facade — no caller broke, no test changed, one PR, and a reusable Claude skill file at the end.
-
remote
Iftar at Apetit: The Sarajevo Team Picks a Menu
One evening in March the Sarajevo Clearviewers sat down for a Ramadan iftar dinner. The Slack thread that got us to the table is the honest picture of how the team actually organizes itself: informal, patient, and mostly saying 'svejedno.'
-
jwt
How a JWT Audience Map Saved a CORS Mistake: A Defense-in-Depth Case Study
On a client's API, a CORS wildcard looked like a HIGH severity finding — until we tried to actually exploit it. A second, independent JWT audience check turned a trivially exploitable bug into one that required a much harder prerequisite.
-
react native
Asking For Notification Permission: The Second Time Is the Wrong Time
iOS gives you exactly one shot at the native permission prompt. Here's the simple screen we show first, so users see what they'll get before the OS asks the question.
-
devsecops
From DevOps to DevSecOps: How I Became Clearview's In-House Pen-Tester
How we built an in-sprint pen-tester role into every engagement — the DevSecOps handoff, the two decades of DevOps that led to it, and the OWASP Top 10 categories that show up first in real client APIs.
-
application development
An Event-Driven Architecture Case Study: Lessons from a Real-World Application
A decade of Clearview engineering for a confidential awards group, and the event-driven AWS architecture that keeps it observable.


No newsletter dance. Three honest ways in.
Long-form essays land here when there's something worth saying. Pick whichever channel fits.
-
For readers
Subscribe via RSS
Your reader pulls new essays as they appear. Per-author feeds live at
RSS feed/authors/<name>/feed.xml. -
For listeners
Founder Vision podcast
Brett interviews founders and operators on the messy middle of building a company.
foundervision.clearview.team -
For writers
Join Clearview Team
We add bylines when the work earns it. The careers page is the place to start — engineers, operators, designers.
View open roles
Or just email us — we read everything.