#security
5 essays on security from the people writing in Remote Since Forever.
- Essays
- 5
- Contributors
- 1
- First filed
- Jul 2026
- Latest
- Sep 2026
-
aws
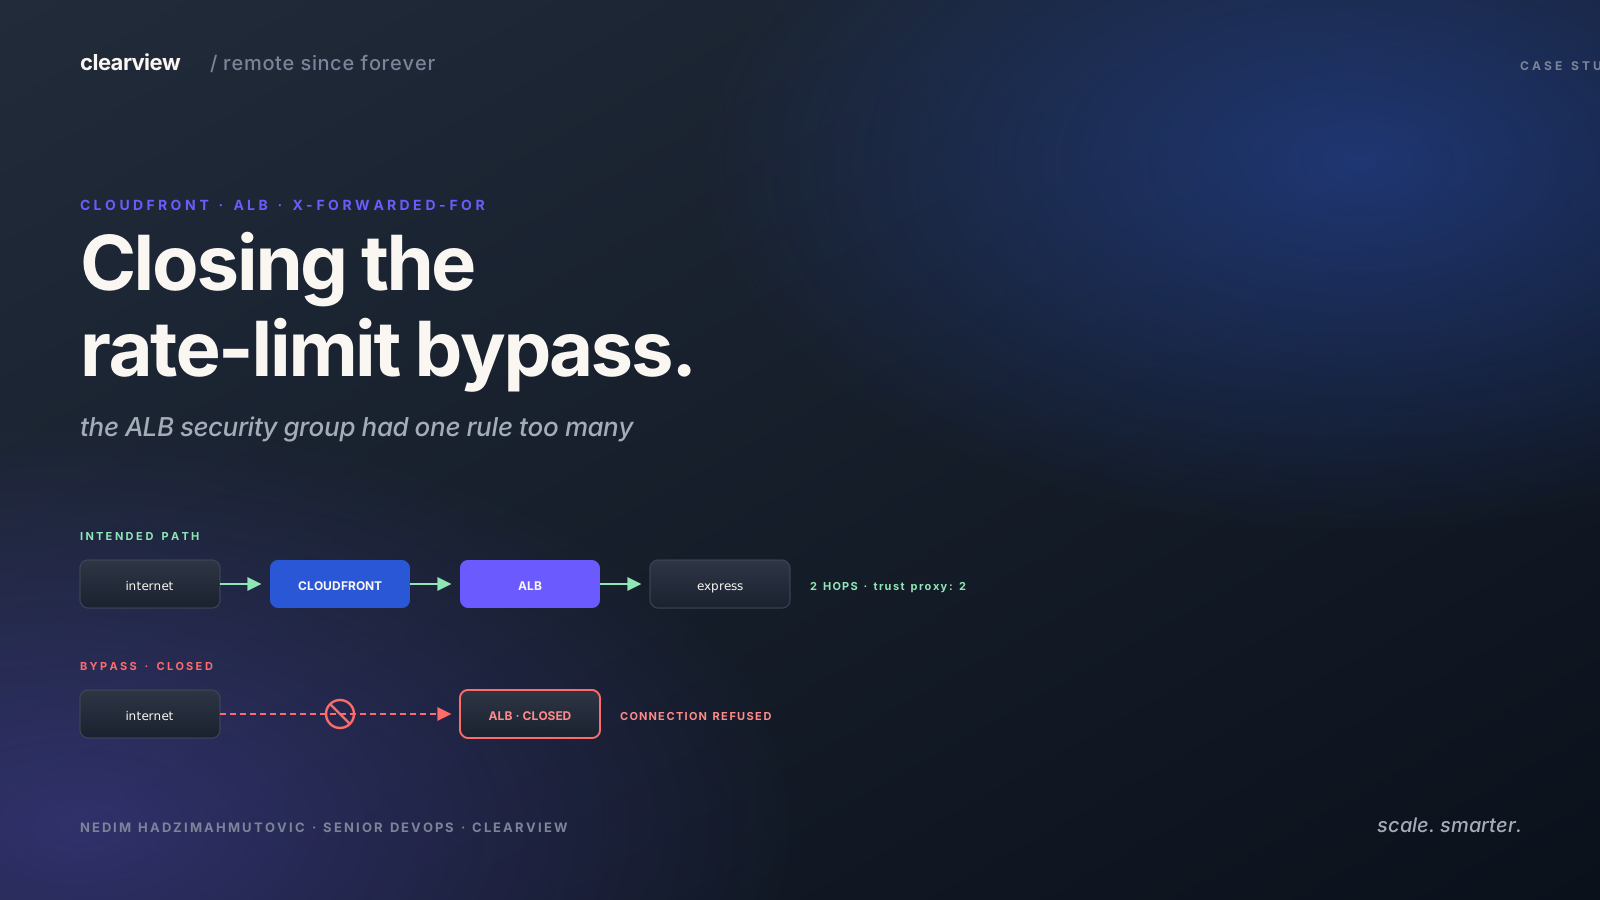
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
-
express
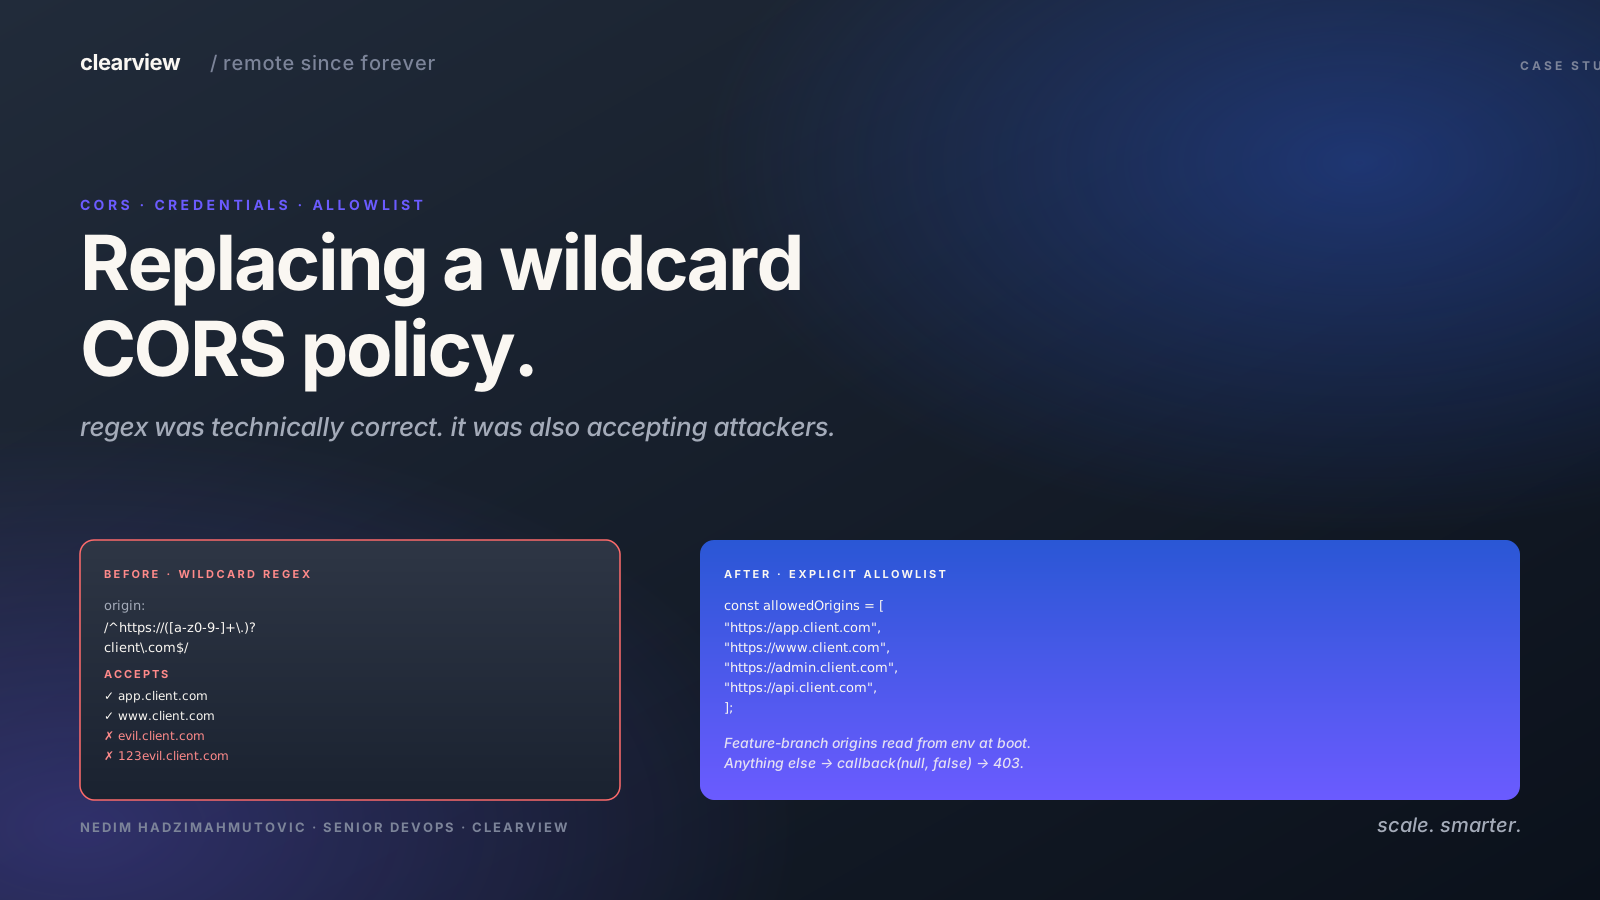
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
-
aws
How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.
-
jwt
How a JWT Audience Map Saved a CORS Mistake: A Defense-in-Depth Case Study
On a client's API, a CORS wildcard looked like a HIGH severity finding — until we tried to actually exploit it. A second, independent JWT audience check turned a trivially exploitable bug into one that required a much harder prerequisite.
-
devsecops
From DevOps to DevSecOps: How I Became Clearview's In-House Pen-Tester
How we built an in-sprint pen-tester role into every engagement — the DevSecOps handoff, the two decades of DevOps that led to it, and the OWASP Top 10 categories that show up first in real client APIs.


No essays match that search.