Web API Security Case Studies
Real Clearview engagements where a client's public API had a securityfinding, and how we closed each one — an Express cors allowlist thatholds up under an escaped-dot regex, a JWT audience map as adefence-in-depth layer, a rate-limit bypass via X-Forwarded-Forspoofing, IAM boundary tightening on a browser-direct S3 upload, and acovert header leak through a CloudFront custom error page. Each postbelow is buyer-shaped: what broke, what we shipped, and what it wouldtake to run on yours.
- Essays
- 3
- Contributors
- 1
- First filed
- Jul 2026
- Latest
- Aug 2026
Start with these
-
Start here
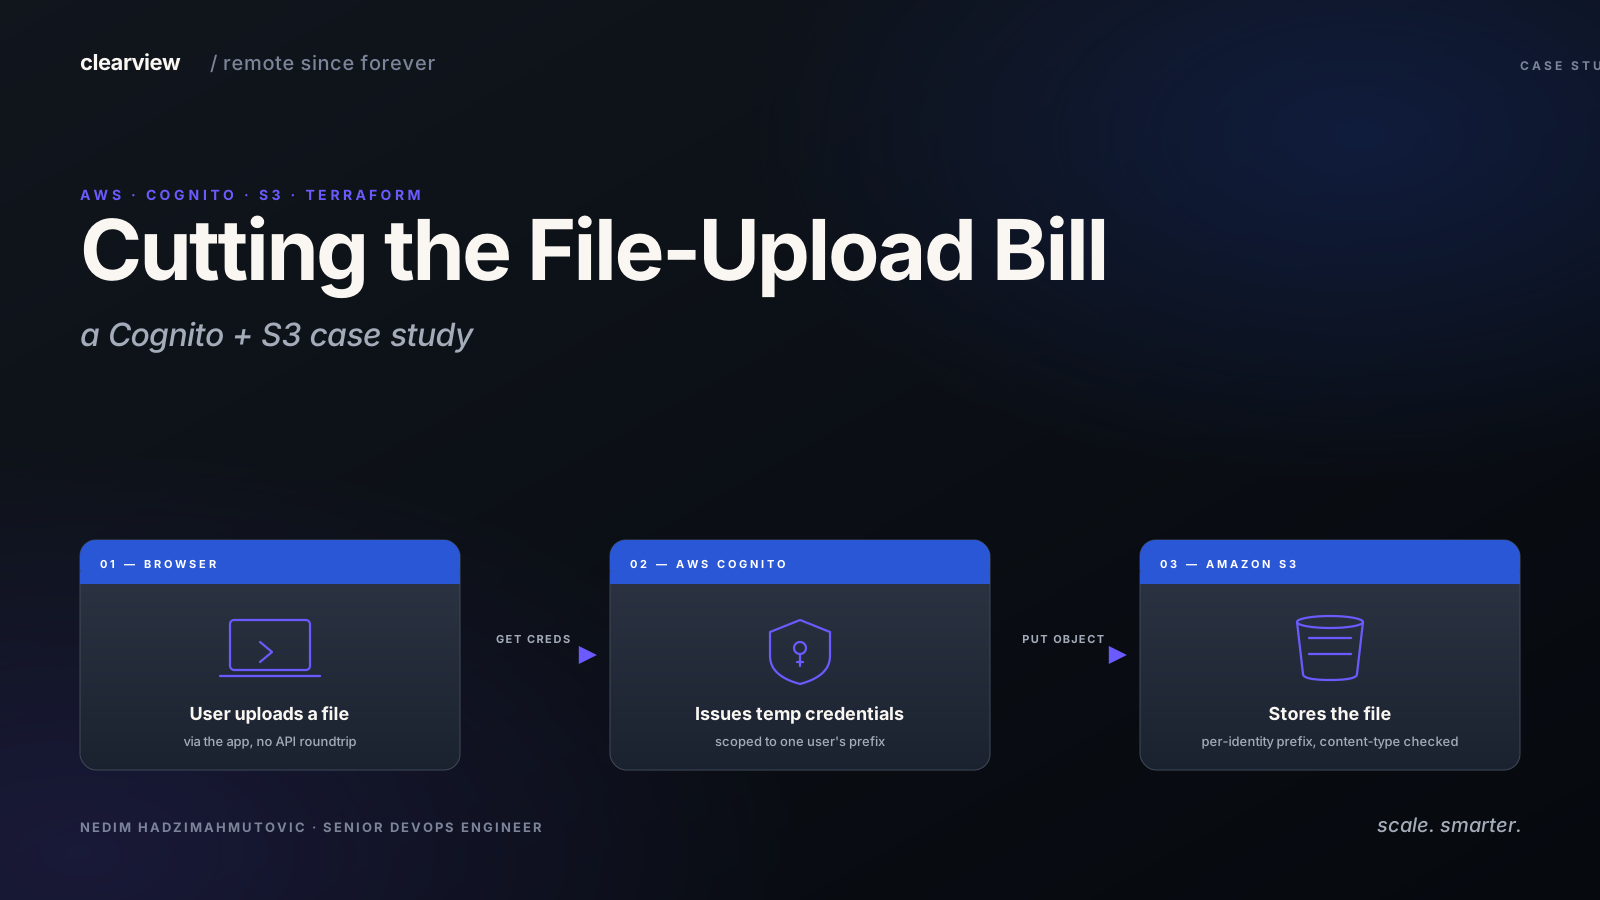
Cutting the File-Upload Bill: A Cognito + S3 Case Study
IAM-scoped browser-direct S3 upload — tightens the trust boundary and cuts the bill.
The rest of the catalog
-
aws
How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.
-
jwt
How a JWT Audience Map Saved a CORS Mistake: A Defense-in-Depth Case Study
Why a second control at a different layer turns a HIGH finding into a MEDIUM.


No essays match that search.