You've sailed past the edge of the map.
There's no essay at that address. A link might have gone stale, or we renamed something in the archives. Either way — here's a bearing back to shore.
Or drop anchor on one of these
-
aws
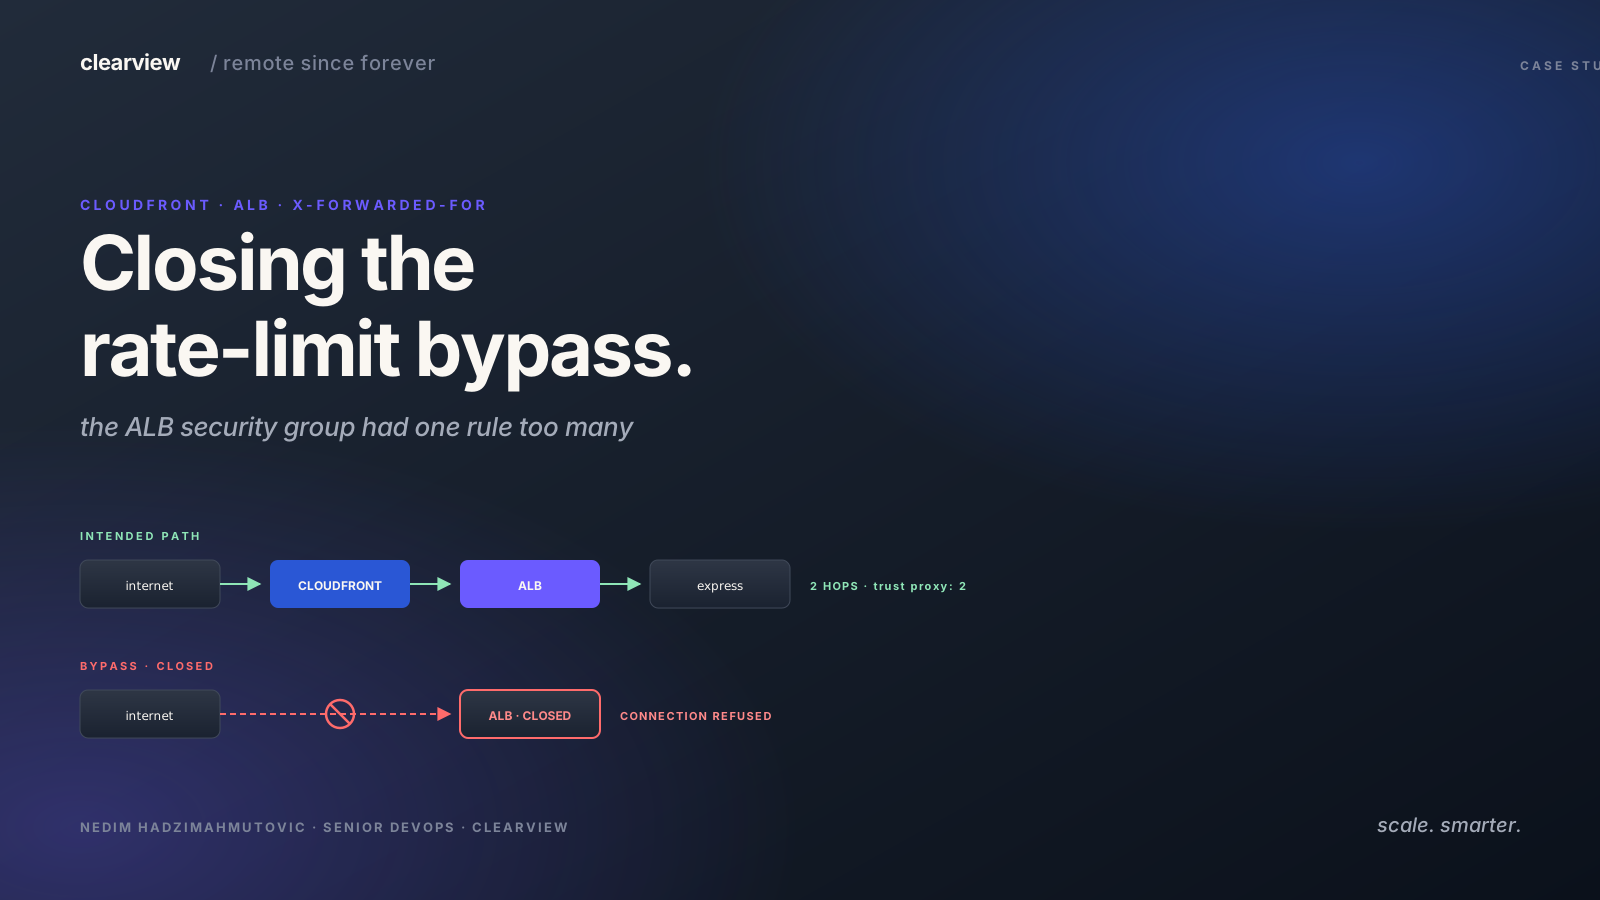
Closing the Rate-Limit Bypass: A CloudFront + ALB Case Study
How we closed an `X-Forwarded-For` spoofing bypass on an AWS WAF rate-limit rule — CloudFront custom secret header, ALB origin verification, and a composite-key rate-based rule that actually counts real clients.
-
express
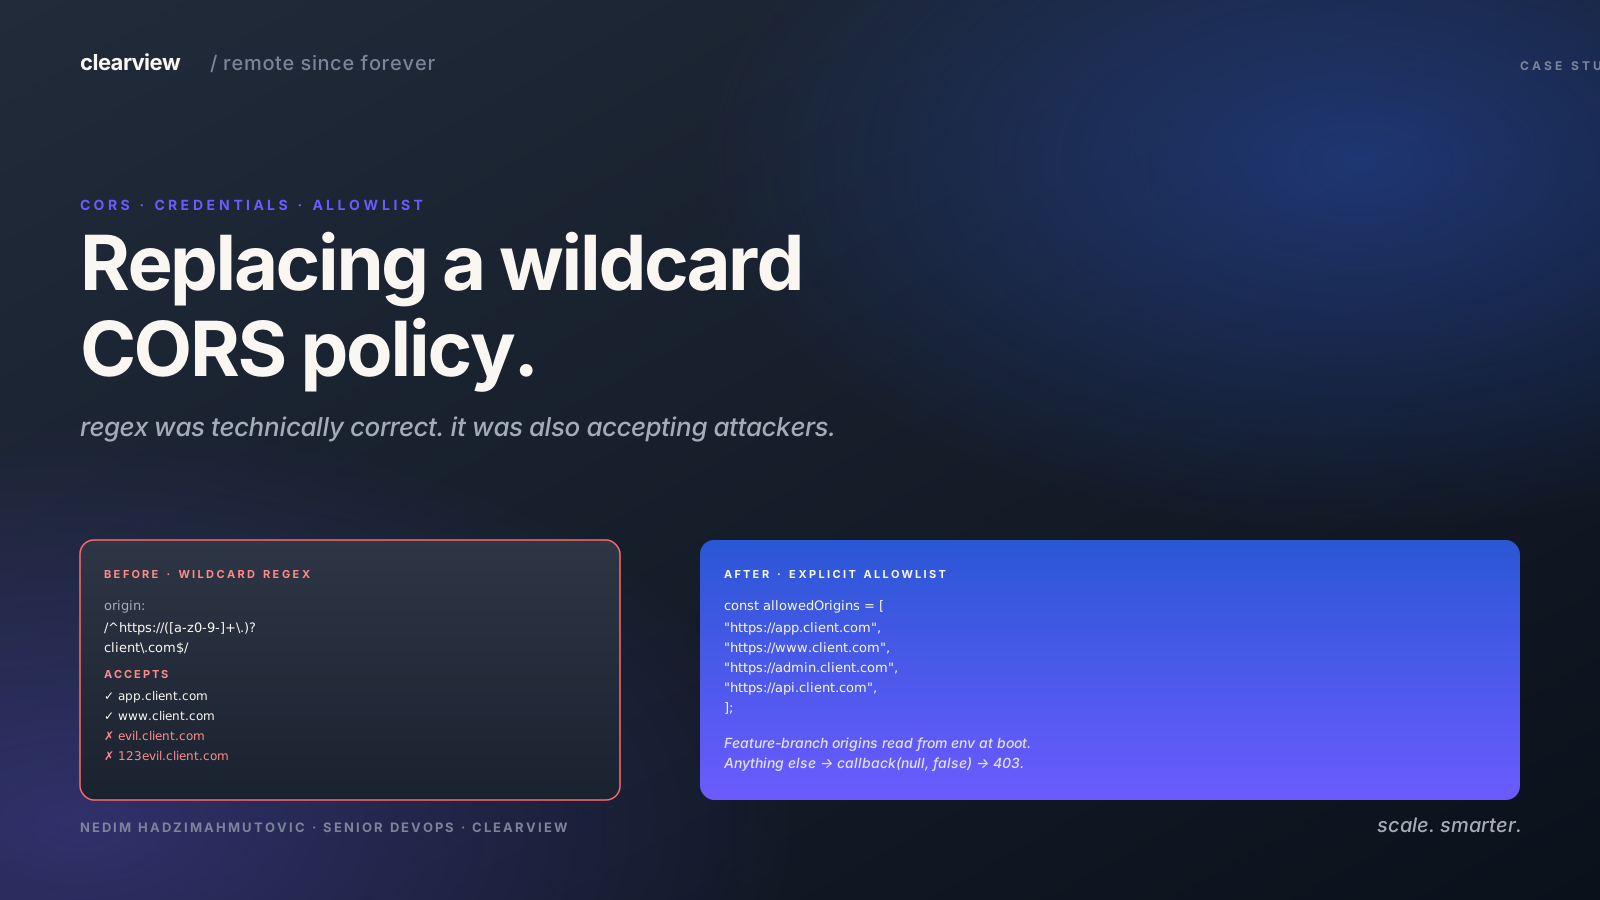
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
-
aws
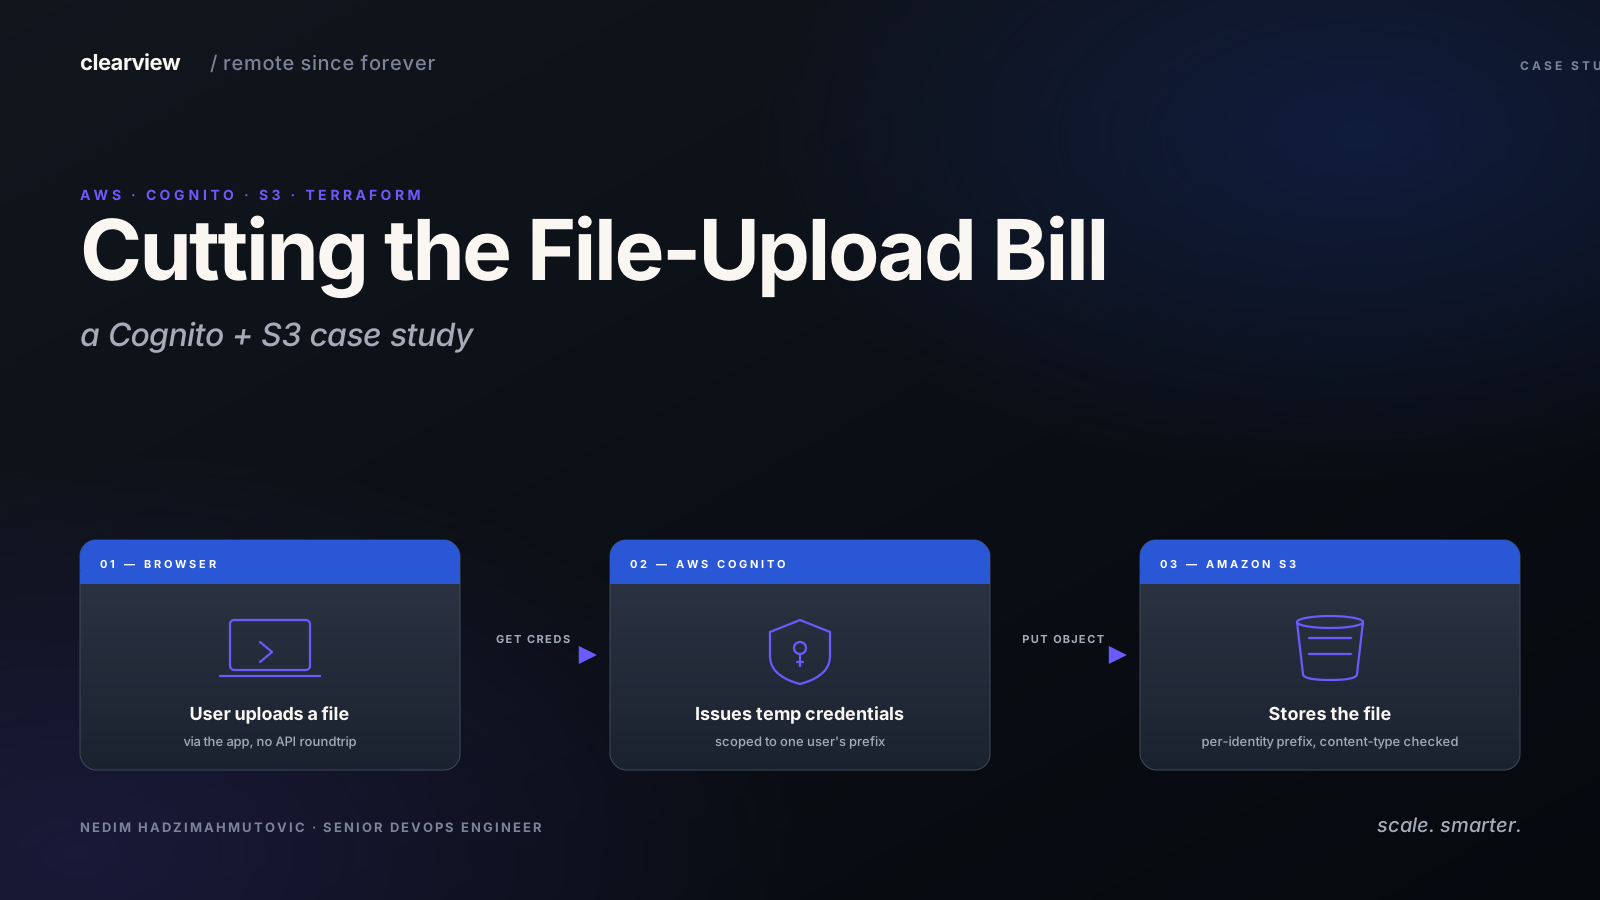
Cutting the File-Upload Bill: A Cognito + S3 Case Study
How we replaced a hosted upload widget with native Cognito and S3, kept the browser uploading straight to the bucket, and brought the monthly invoice down.