#apisecurity
3 essays on api security from the people writing in Remote Since Forever.
- Essays
- 3
- Contributors
- 1
- First filed
- Jul 2026
- Latest
- Aug 2026
-
express
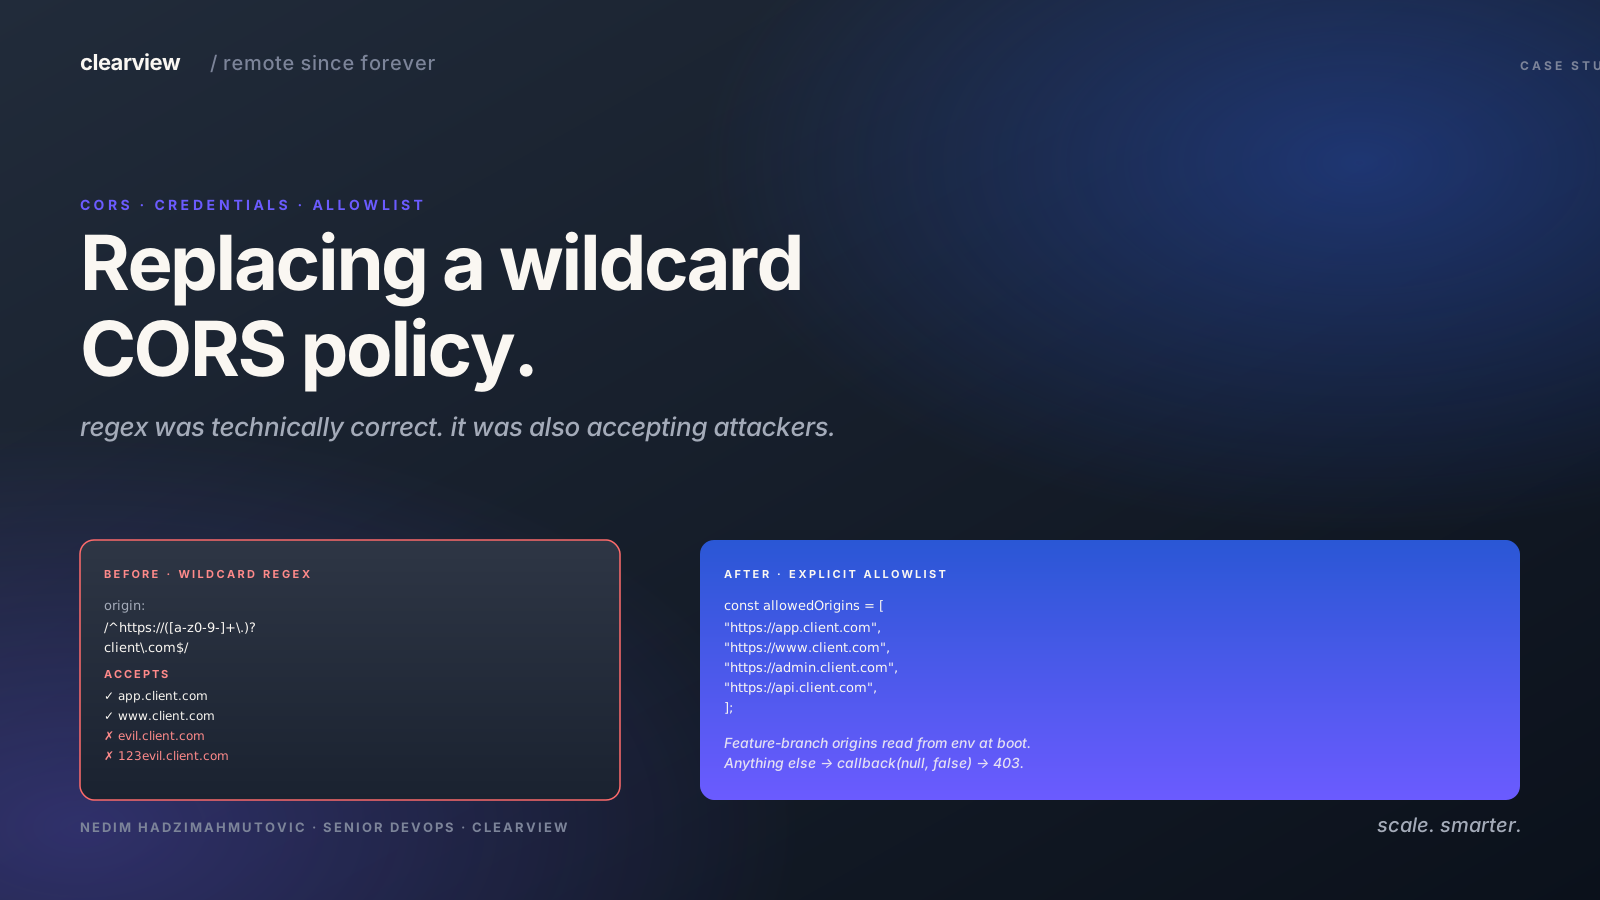
Replacing a Wildcard CORS Policy: An Express Allowlist Case Study
How we replaced a permissive Express `cors` regex with a strict allowlist — escaped-dot origin matching, `Vary: Origin` on every response, and no more CWE-942 finding on the pen-test report.
-
aws
How a CloudFront Custom Error Page Leaked JWTs to S3: A Case Study
A pen-test curl found CloudFront forwarding `Authorization` headers to the S3 error-page bucket, where S3 reflected every JWT back in its XML error response. Two lines of Terraform closed it across sixteen distributions.
-
jwt
How a JWT Audience Map Saved a CORS Mistake: A Defense-in-Depth Case Study
On a client's API, a CORS wildcard looked like a HIGH severity finding — until we tried to actually exploit it. A second, independent JWT audience check turned a trivially exploitable bug into one that required a much harder prerequisite.


No essays match that search.